Posts

marco@thinkst.com

Image
In 2009 I wrote a post on recruiting and mentioned " the T-shirt Test ". It read: The T-Shirt test is simply to ask yourself: "how will i feel standing at a conference, with this guy next to me wearing my company T-Shirt". If you don't like the thought, you shouldn't make the hire. I still feel strongly about the T-Shirt test, and feel really strongly about the importance of company culture which makes it crazily cool to officially welcome Marco Slaviero as the newest member of Thinkst. I worked with Marco for several years at SensePost, and we have had some über fruitful collaboration during (and after) that period. I could wax lyrical for a while, but we believe the results will be self evident. Watch this space!

Penetration Testing considered harmful today

Image
Early last year we presented at 44con with a talk titled: " Penetration Testing considered harmful today ". 44con have just released the video so we figured it was worth a quick recap (for anyone not willing to tolerate the whiny voice!) The original slides (in PDF) are available ( here ) The central thesis of the talk is that penetration testing has established itself as a necessary activity for securing a network and is now pushed forward by a multi million dollar industry despite the clear signs that it is not helping all that much. ( Read the annotated slides here ) Watch the video here :

Chrome Extension for gpg in Gmail

Image
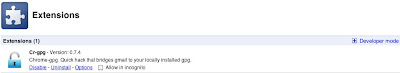
Last month we released an alpha version of cr-gpg . This is a simple Chrome extension to enable gpg functionality in gmail (or Apps for Domains). (If you don't know what gpg is, you should first read this and this .) Installation : You can grab the extension from [ here ] and a double click should install it , after the install is completed you should see the image above if you navigate to chrome://extensions : Options : Once you have installed the plugin, there are 2 required configuration options: 1) Directory with gpg binary 2) Temp folder path (writable by the browser) (cr-gpg simply calls out to the gpg installation on your machine. Option [1] therefore is asking where it can find the gpg executable, and Option [2] is looking for a scratch directory to do its work). (We make some effort to ensure that the temp directory is well maintained). You should be able to click "Use Default" on most installations. The "Encrypt to self" option is fairly self explana...

BlackHat according to Twitter

Image
For the first time in a decade I didn't attend BlackHat USA in Las Vegas. I learned that South Africa in August is much colder than i recalled, but also had the chance to observe the conference from through a twitter-lense. It seemed as if there was more talk about parties, than content so I decided to grab all the tweets i could (#blackhat through the twitter search API) to do some simple grouping*. Whats clear straight off is that my intuition was wrong. Although party talk makes up a significant percent of all tweets, tweets about "talks & training" clearly dominate. (This possibly means that i need to start following a better class of hax0r) A quick explanation of the grouping (which was done pretty coarsely): Talks & Training : Tweets related to a talk (or training session) Misc : (General catch-all for tweets about coffee / *) Spam : People who stole the hashtag to push traffic to their own site (used by quite a few big name vendors to draw traffic to their ...

ShoulderPad Slashdotted! (and two clarifications)

(because we can't have enough posts with exclamation marks in them) Our previous post (and research ) seemed to go by pretty silently initially and then suddenly was everywhere. Andy Greenberg wrote a piece over at Forbes which really does deserve special mention. Tech journalists so often sensationalize security stories that many security researchers are quite afraid to even talk them. I certainly was, but his piece was fair, balanced and covered all the interesting points. +1 to him. The Forbes post was copied almost verbatim by a ton of other " news " sites on the 'net, but we beamed with some measure of geek pride at making the front page of Slashdot (and for featuring on the front page of Hacker News , The Unofficial Apple Weblog and HackADay ). Two Clarifications: A surprising number of people reacted to the work (on slashdot, or other forums) with: " FAKE ! The iPad Keyboard is not black!". One thread even went into detail about how this meant th...

On-screen Keyboards Considered Harmful

Image
(aka: Shoulder Surfing: There's an App for that!) We rarely talk about it these days, but shoulder surfing is a pretty old (but reliable) attack. This is why most password prompts are masked. Many modern mobiles (and tablets) however will highlight keys pressed on the keyboard making old style shoulder surfing attacks trivial (and reasonably automatable) again. In an effort to (help) bring back the 90's we decided to do some fiddling and built a quick app(on top of the awesome OpenCV framework) to automate shoulder surfing against iPads. (You can read more about it [ here ], download a short pdf on it [ here ] or just watch the youtube video below (but we think the pdf is more fun!)) There are a few more videos (available after the break) This was an early version of shoulderPad. We assumed we had won by simply locating the blue key-presses. One of the previewers asked: "Are you deliberately moving your fingers out of the way?" We decided to answer by quickly typing A...

Simple Graphs with Arbor.js

Image
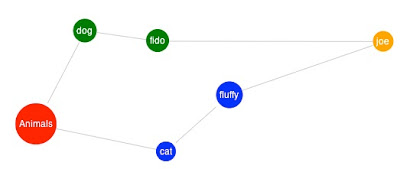
We recently released a tool at http://cc.thinkst.com to capture and collect infosec conference details. We commented on it [ here ]. One of the cooler components of it, is the ability to view the relationships between speakers/researchers who have collaborated. This post is a quick introduction to the library we used to build our graphs, with enough info to get you up and running in minutes. As I mentioned, we use ArborJS library which is a a graph visualization library using web workers and the popular jQuery . The API is really well documented [ here ] but like most people, I learn best by example (and there are precious few of these). Hopefully this post will fill that niche, and by the end of it you should have a basic understanding of how to use arbor.js in your project. Our Aim: We will be building a simple contrived example as seen in the image above. Project setup : Create a new html page and include script references to the following libraries (Download them from the links...